
With the capability of gathering more patient data than ever before, there’s a double-edged sword. This data has the potential to inform better patient treatment, but it also needs to be handled with care. The pros should outweigh the cons.
For example, medical alert system costs, in terms of price and peace of mind, shouldn’t sacrifice data security. Let’s explore the world of data retention and compliance for health-adjacent data.
Health-Adjacent Data Explained
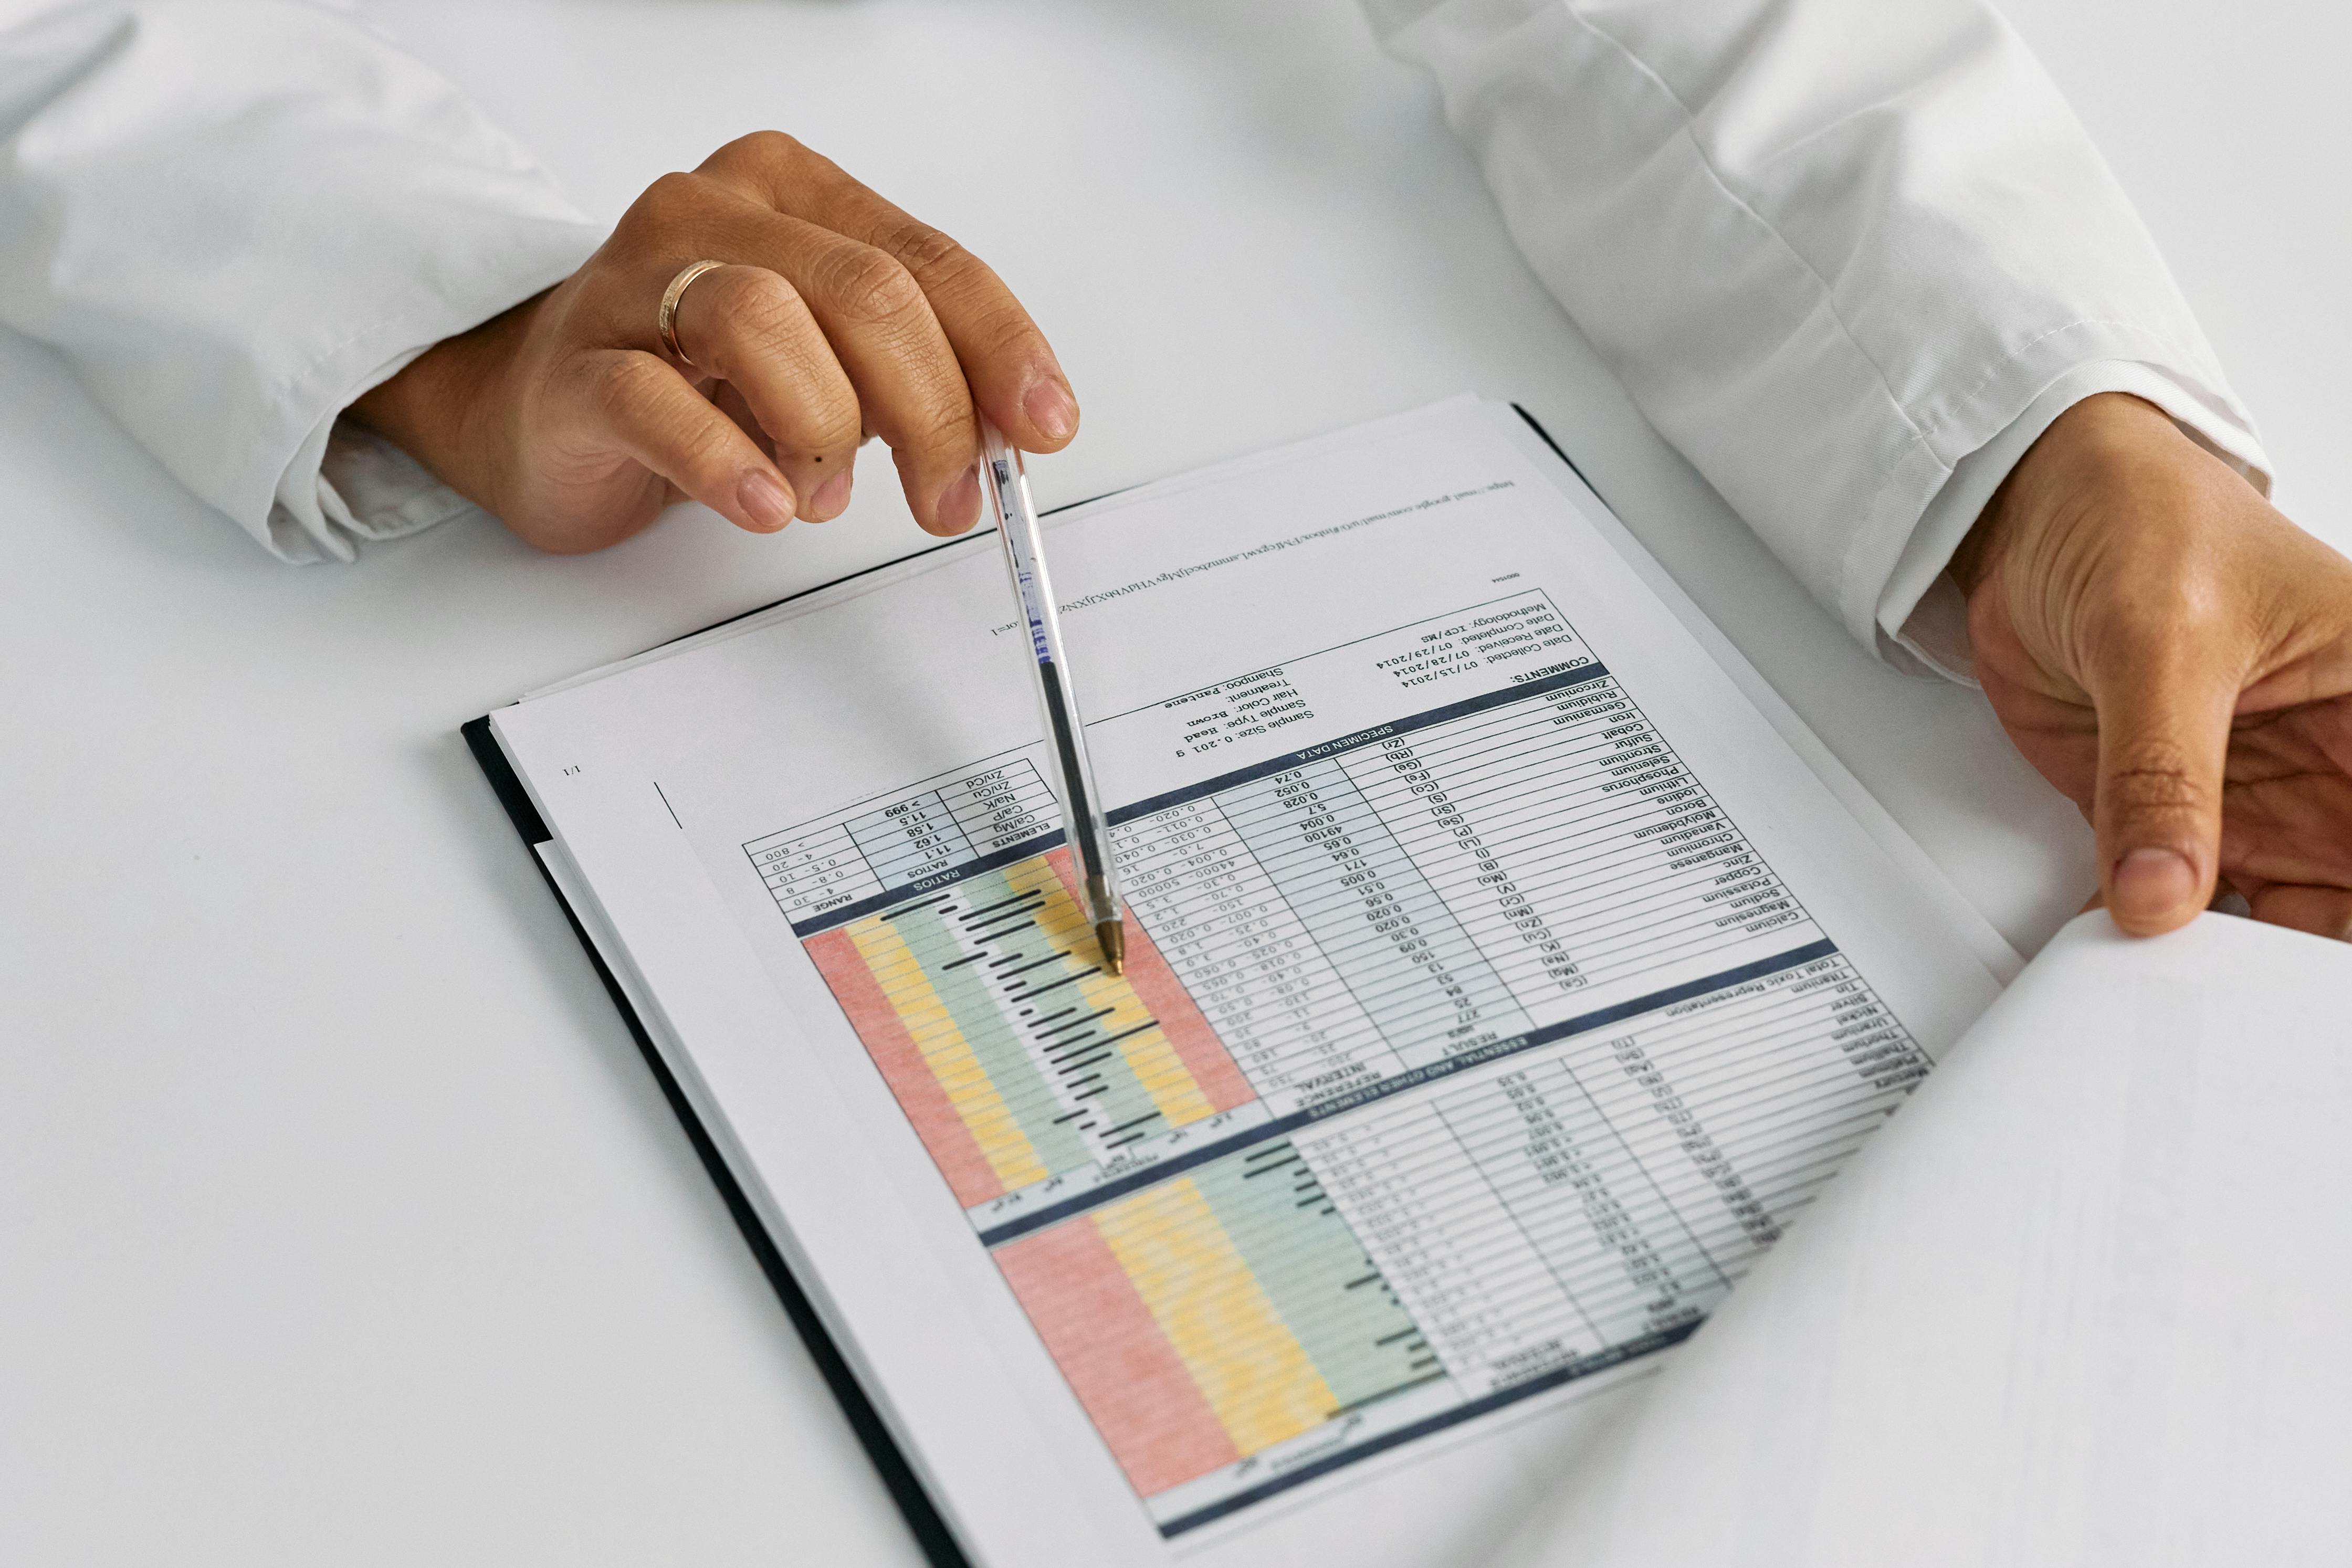
What exactly is health-adjacent data? Well, it’s any data that doesn’t fall under the shielding umbrella of protected health information and compliance regulations. While this data is similar to traditional healthcare information, it is not the same. However, it can inform treatment and help shape decisions.
Examples of Health-Adjacent Data Information
Typical examples of health-adjacent data collection devices include wearable health technology, such as monitors and trackers. These are commonly used to assess sleep quality, fitness levels, and other metrics that could be useful to influence diagnoses.
Other examples of where health-adjacent data is gathered include nutrition services and mental health platforms. This can be extracted through mobile apps and online forms to help personalize the service.
What is HIPAA and PHI?
When discussing health-adjacent data, the terms HIPAA and PHI regularly feature. Knowing what these acronyms stand for helps clarify how health-adjacent data differs from traditional medical information found in patient charts and files.
HIPAA compliance
The Health Insurance Portability and Accountability Act, or HIPAA for short, is a law that was passed in the US back in 1996. This regulation governs how medical data is both used and kept. The types of medical data that are controlled by this act are PHI or Protected Health Information.
What counts as PHI?
Protected Health Information or PHI comprises health data such as billing information, medical records, and lab test results. So, any health, treatment, or payment details that can be used to identify the patient are classed as PHI.
Why is Data Retention Important?
An individual’s health information has an important place in future treatments and medical interventions. Therefore, retaining all relevant medical data helps with continuity of care.
Another reason why retaining data is a useful practice is to safeguard medical professionals. Having access to this data can protect practitioners from medical malpractice claims and legal disputes.
Data: When to Delete and When to Retain
Data does require careful management to ensure it doesn’t fall into the wrong hands. If data is incorrectly retained or kept longer than is necessary, what happens? Well, it could endanger patient confidentiality and put healthcare practitioners at risk, too.
Data should be deleted when it is no longer relevant to keep the information. For example, when the patient hasn’t had interactions with the healthcare provider for many years or has switched services, then there is no need to hang onto the information. This reduces the risk of data breaches and also the storage costs of keeping data.
Information should be retained when there is a legal obligation to do so. So, if state laws require data to be kept for a specific amount of time, then careful retention of data is a must. Data should always be retained in line with data protection regulations.
Then there’s the issue of data storage. Not only are healthcare businesses footing the bill for keeping hold of all this data, but they are also at risk of negatively affecting efficiency. If a database is clean and clutter-free, employees can quickly and efficiently access the data. This improves customer service and minimizes errors.
How to Avoid Making Data Retention and Compliance Mistakes
Data retention isn’t as difficult to manage as you would think. However, it’s all down to how well you know the regulations and being aware of the common mistakes and how to avoid them.
Not keeping up to date with current regulations is where many healthcare businesses can trip up. As regulations change, so should your protocols. This applies to the retention periods and how to securely hold onto data.
Although data should be kept as long as is necessary to ensure continuity of care. It should be stored in line with industry and government regulations. Keeping data longer, just in case, can lead to data protection issues and put healthcare businesses in danger of damaging lawsuits.
Resource: YouTube
Best Practice to Stay on Top of Data Compliance
In addition to staying in the loop when regulations change, it’s important to keep on top of audits.
Carrying out regular audits and reviewing data retention protocols annually is a healthcare business’s best line of defense against malpractice claims. This also reinforces patient trust in the service you provide. They are safe in the knowledge that their important health data is well protected.
Another way to stay one step ahead of regulations is to use the best resources available to you. Perhaps by hiring data compliance experts to offer advice, or maybe you turn to automation and new technology. Seeking the right support, this makes it easier to stay on top of data compliance.

This content is brought to you by the FingerLakes1.com Team. Support our mission by visiting www.patreon.com/fl1 or learn how you send us your local content here.